Grubhub has confirmed a data breach involving unauthorized access to its internal systems, amid claims of extortion from the ShinyHunters hacking group demanding Bitcoin payments to prevent the release of stolen data.
Food delivery platform Grubhub has officially acknowledged a recent data breach after unauthorized individuals accessed parts of its internal systems. This confirmation comes as sources report that the company is facing extortion demands related to the stolen data.
In a statement to BleepingComputer, Grubhub indicated that it quickly detected and halted the unauthorized activity. “We’re aware of unauthorized individuals who recently downloaded data from certain Grubhub systems,” the company stated. “We quickly investigated, stopped the activity, and are taking steps to further increase our security posture.”
While Grubhub assured that sensitive information such as financial details and order history was not compromised, the company did not provide additional information regarding the timing of the breach or the extent of customer data involved. Furthermore, it has not confirmed whether it is currently being extorted.
Grubhub has engaged a third-party cybersecurity firm and notified law enforcement about the incident. However, the company has remained largely silent on further details, raising concerns given its recent security history. Just last month, Grubhub was linked to scam emails sent from its own b.grubhub.com subdomain, which promoted a cryptocurrency scam that promised large returns on Bitcoin investments. Grubhub stated that it contained the incident and blocked further unauthorized emails but did not clarify if this event is related to the current breach.
According to multiple sources cited by BleepingComputer, the ShinyHunters hacking group is allegedly behind the extortion attempt. The group has not publicly commented on these claims and did not respond when contacted. Sources indicate that the attackers are demanding a Bitcoin payment to prevent the release of stolen data, which reportedly includes older Salesforce records from a breach in February 2025, as well as newer Zendesk data taken during the most recent intrusion. Grubhub utilizes Zendesk for its online customer support system, which handles order issues, account access, and billing questions, making it a significant target for attackers.
Investigators believe that the breach may be connected to credentials stolen during previous Salesloft Drift attacks. In August 2025, threat actors exploited stolen OAuth tokens from Salesloft’s Salesforce integration to access sensitive systems over a 10-day period. A report from Google Threat Intelligence Group, also known as Mandiant, noted that attackers used this stolen data to launch subsequent attacks across multiple platforms. “GTIG observed UNC6395 targeting sensitive credentials such as AWS access keys, passwords, and Snowflake-related access tokens,” Google reported. ShinyHunters has previously claimed responsibility for this campaign, asserting that it stole approximately 1.5 billion records from Salesforce environments linked to numerous companies.
Even though Grubhub maintains that payment data and order history were not affected, support systems often contain personal information. Names, email addresses, and account notes can be sufficient to fuel phishing attacks or identity scams. This incident underscores how older breaches can continue to inflict damage long after the initial attack, as stolen credentials that are not rotated remain a potent entry point for threat actors.
For users of Grubhub or any online delivery service, there are several proactive steps that can be taken to mitigate risks following a breach. First, it is advisable to change your Grubhub password immediately and ensure that it is not reused across other accounts. Reused passwords can provide attackers with an easy pathway into additional accounts. Utilizing a password manager can assist in creating strong, unique logins and securely storing them.
Next, check if your email has been exposed in past breaches. Many password managers include a built-in breach scanner that can verify whether your email address or passwords have appeared in known leaks. If a match is found, promptly change any reused passwords and secure those accounts with new, unique credentials.
Enabling two-factor authentication (2FA) where available adds an additional layer of security when signing in, requiring a code sent to your phone or app. This can help prevent unauthorized access even if a hacker obtains your password.
Be vigilant for emails or texts referencing orders, refunds, or support issues. Attackers often leverage stolen support data to craft messages that appear urgent and legitimate. Avoid clicking links or opening attachments unless you are certain of their authenticity. Strong antivirus software can also help block malicious links and downloads before they cause harm.
Consider using a data removal service to minimize your online footprint. These services assist in removing personal details from data broker sites that attackers may exploit to build profiles. While no service can guarantee complete removal of your data from the internet, employing a data removal service can significantly reduce the information available to scammers.
Be cautious of any cryptocurrency offers associated with familiar companies. Grubhub’s previous link to scam emails promoting crypto schemes illustrates how frequently attackers exploit trusted names. Legitimate companies do not promise quick returns or pressure customers to act immediately.
Regularly monitor your Grubhub account for any unfamiliar activity. Watch for unexpected password reset emails, order confirmations, or support messages that you did not initiate. Attackers often test stolen data quietly before executing larger schemes.
As breaches continue to pose risks, Grubhub’s confirmation highlights the importance of transparency and rapid credential rotation. The lingering effects of past compromises can create new vulnerabilities, emphasizing the need for proactive measures to safeguard personal information.
This incident serves as a reminder of the ongoing challenges in cybersecurity and the necessity for vigilance in protecting personal data. As extortion-driven breaches become more prevalent, customers must remain informed and prepared to act to protect themselves.
For further details, visit BleepingComputer.
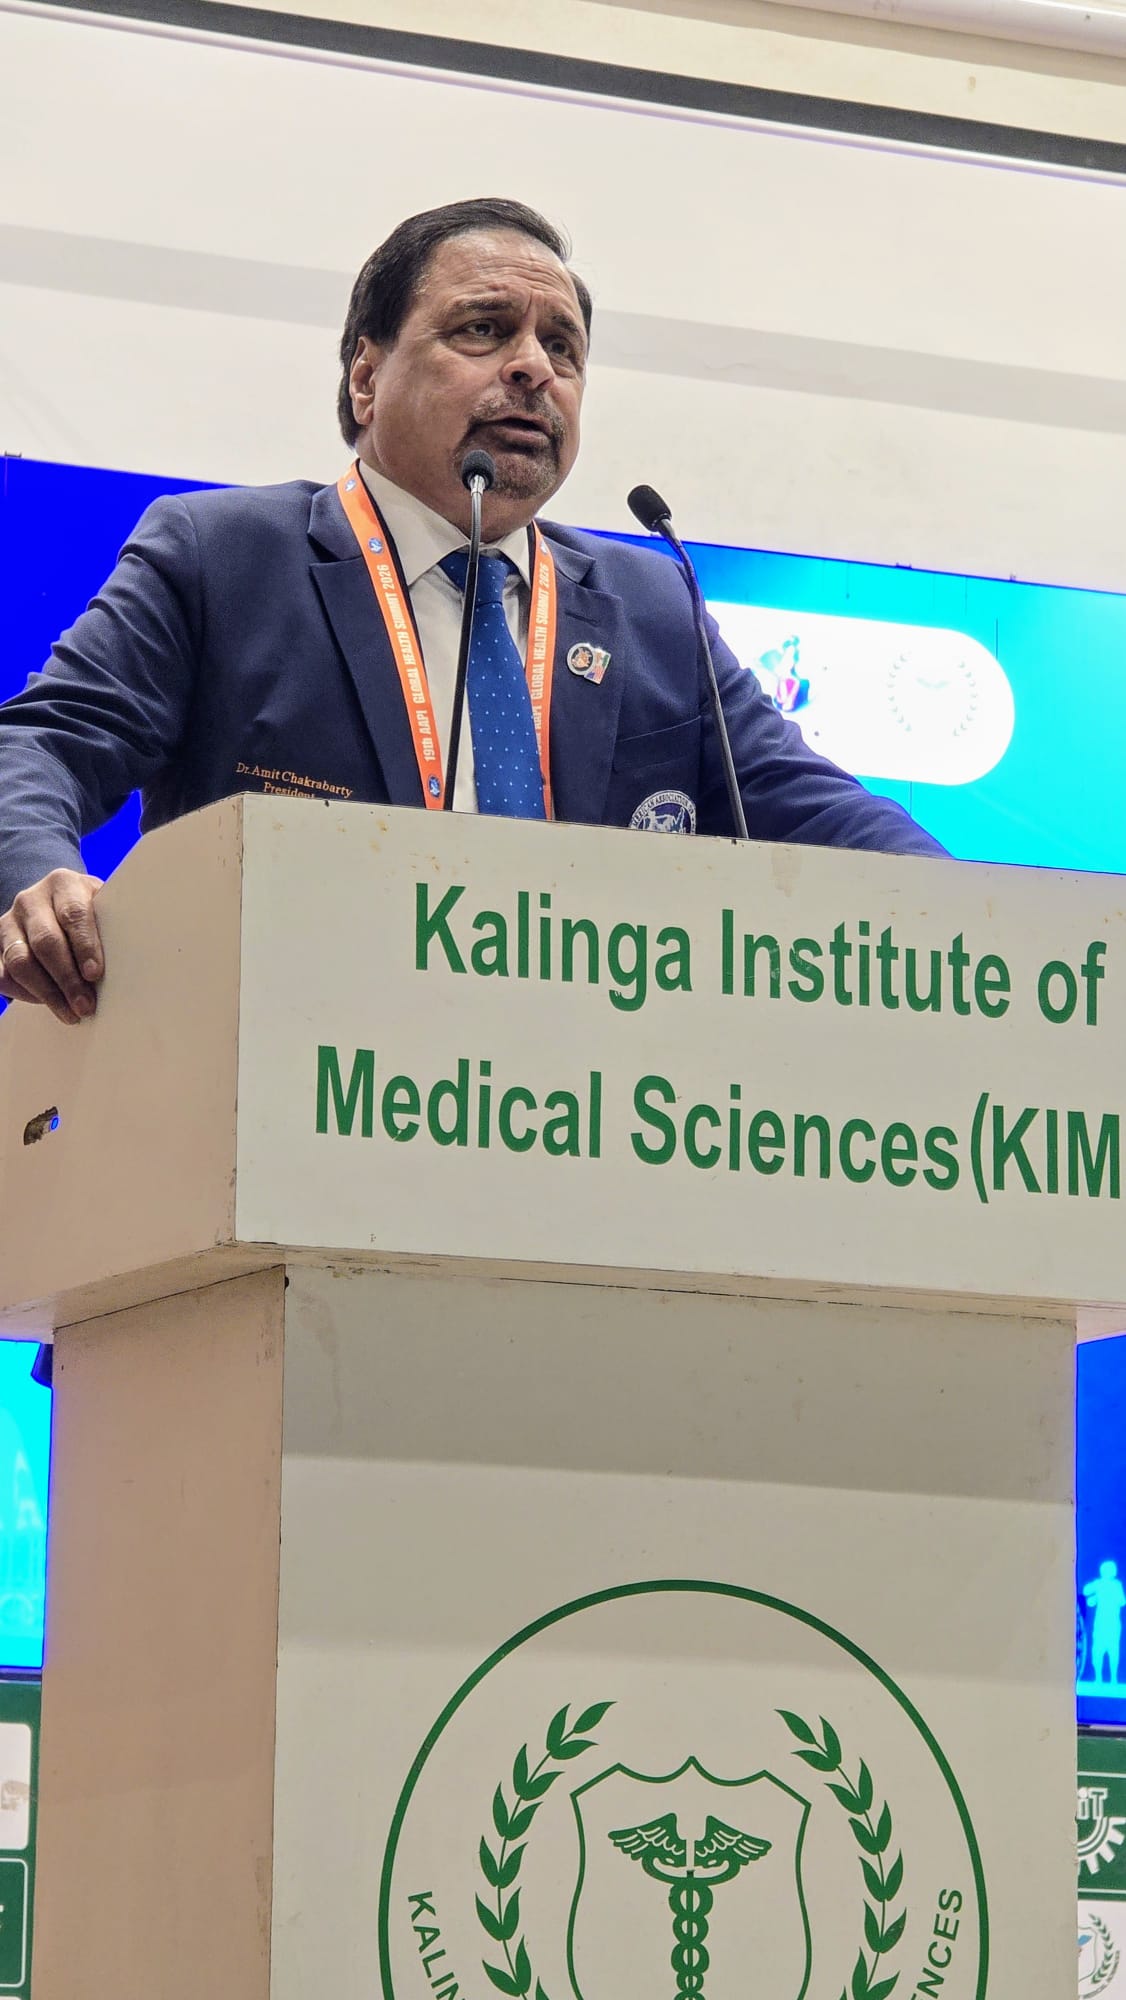 “We received 238 Stem Donors who registrations at our Stem Donor Registry during the Global Healthcare Summit held in Bhubaneshwar, Orissa from Jan 9-11, 2026,” said Dr. Sashi Kuppala, Chair of the Stem Cell Drive. “ To put it in context, we would have had to do 20 drives to get those many registrations in the United States. Thanks to Dr. Amit Chakrabarthy, we successfully launched the project in India.”
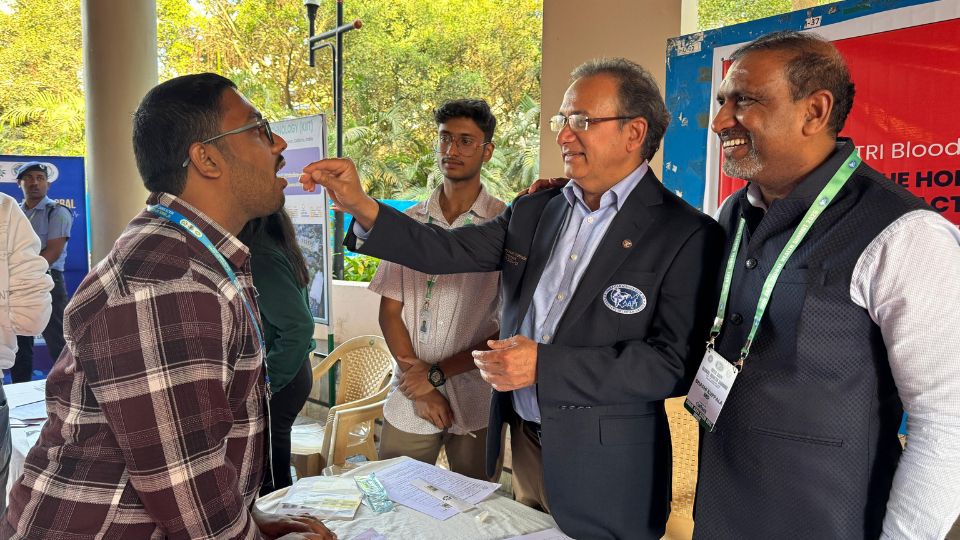 During the inaugural ceremony of GHS, Prof. R C Das, Dean and Principal of KIMS stressed the importance and urged the medical students at KIM to come forward and register for Stem Donorship. The students were then led to pledge and commit to encourage Stem Donorship among the patient population they are committed to serve.
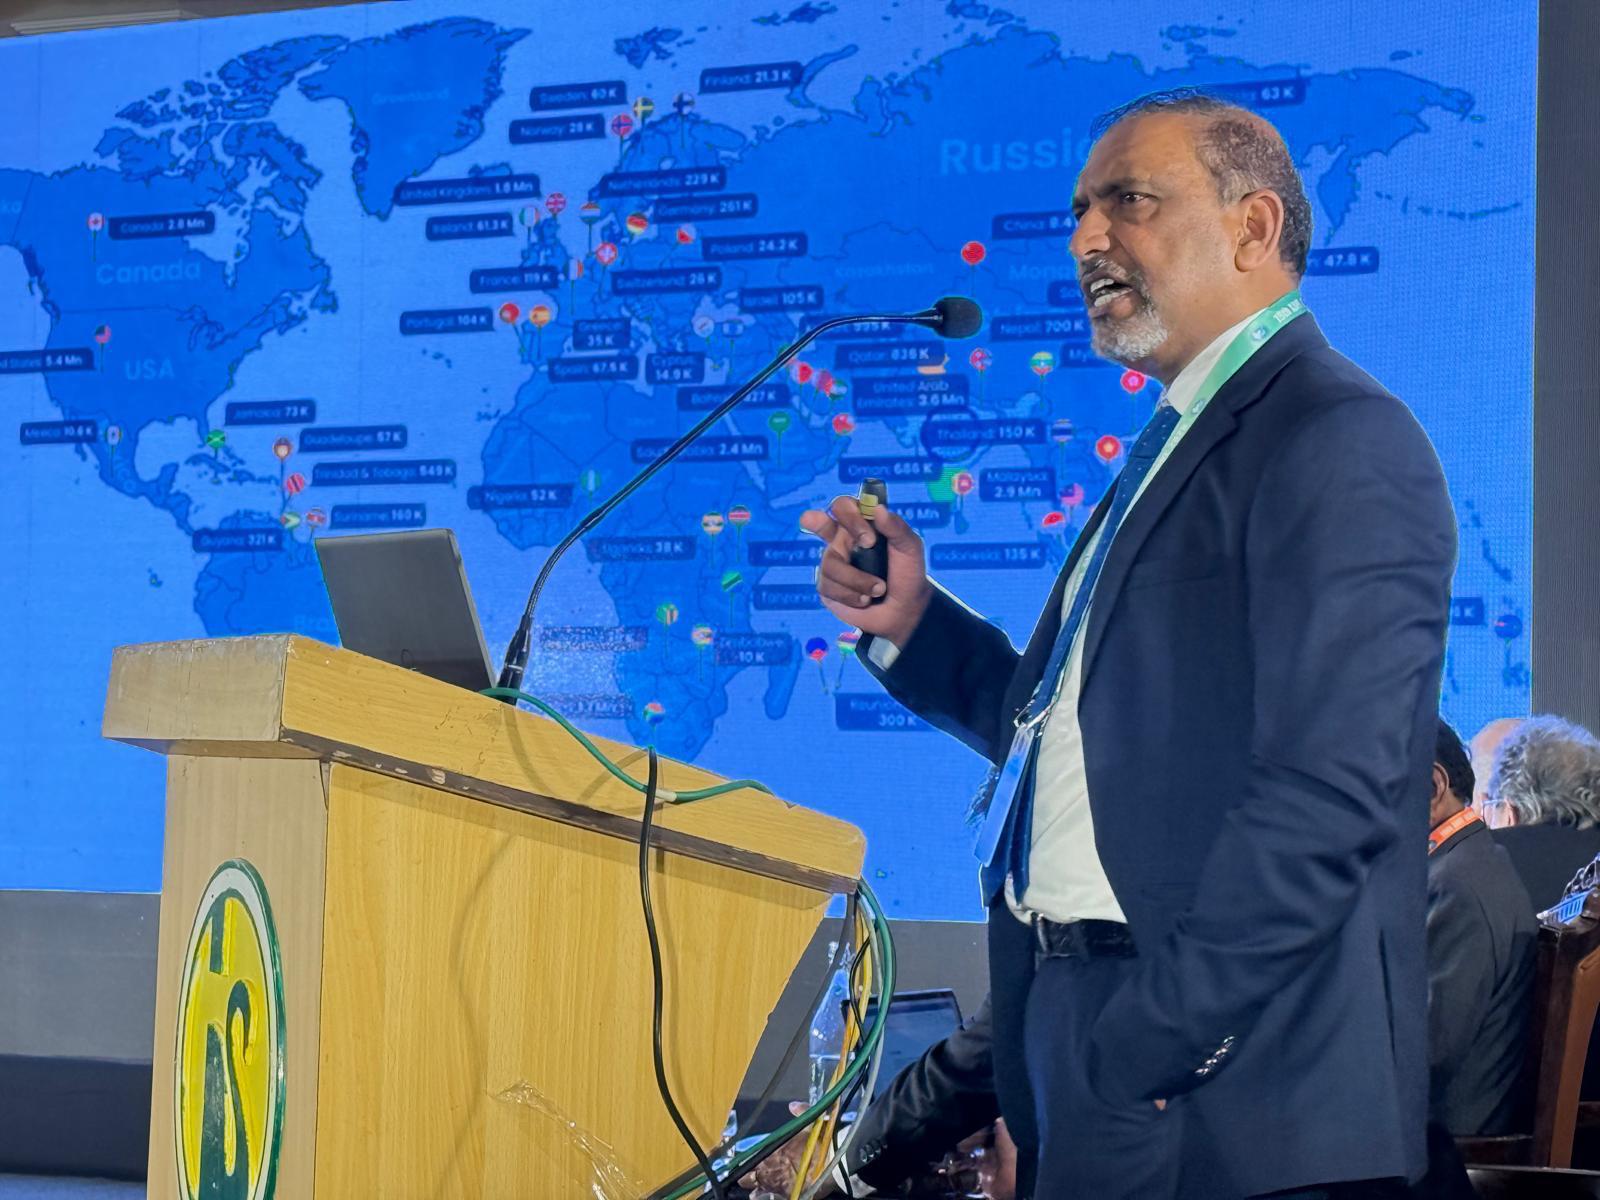 Stem cells are one of the treatment options for certain types of cancers. HLA typing, based on which stem cell donors and patients are matched is ethnicity specific. Indian patients have higher chances of matching with Indian donors. Unfortunately, Indian donor pool is very limited, making it difficult for patients to find a proper match. Moreover, until now, patients and their families are doing these drives on their own to find the match in addition to dealing with the diagnosis. There has been no unified push to increase the Indian donor pool.
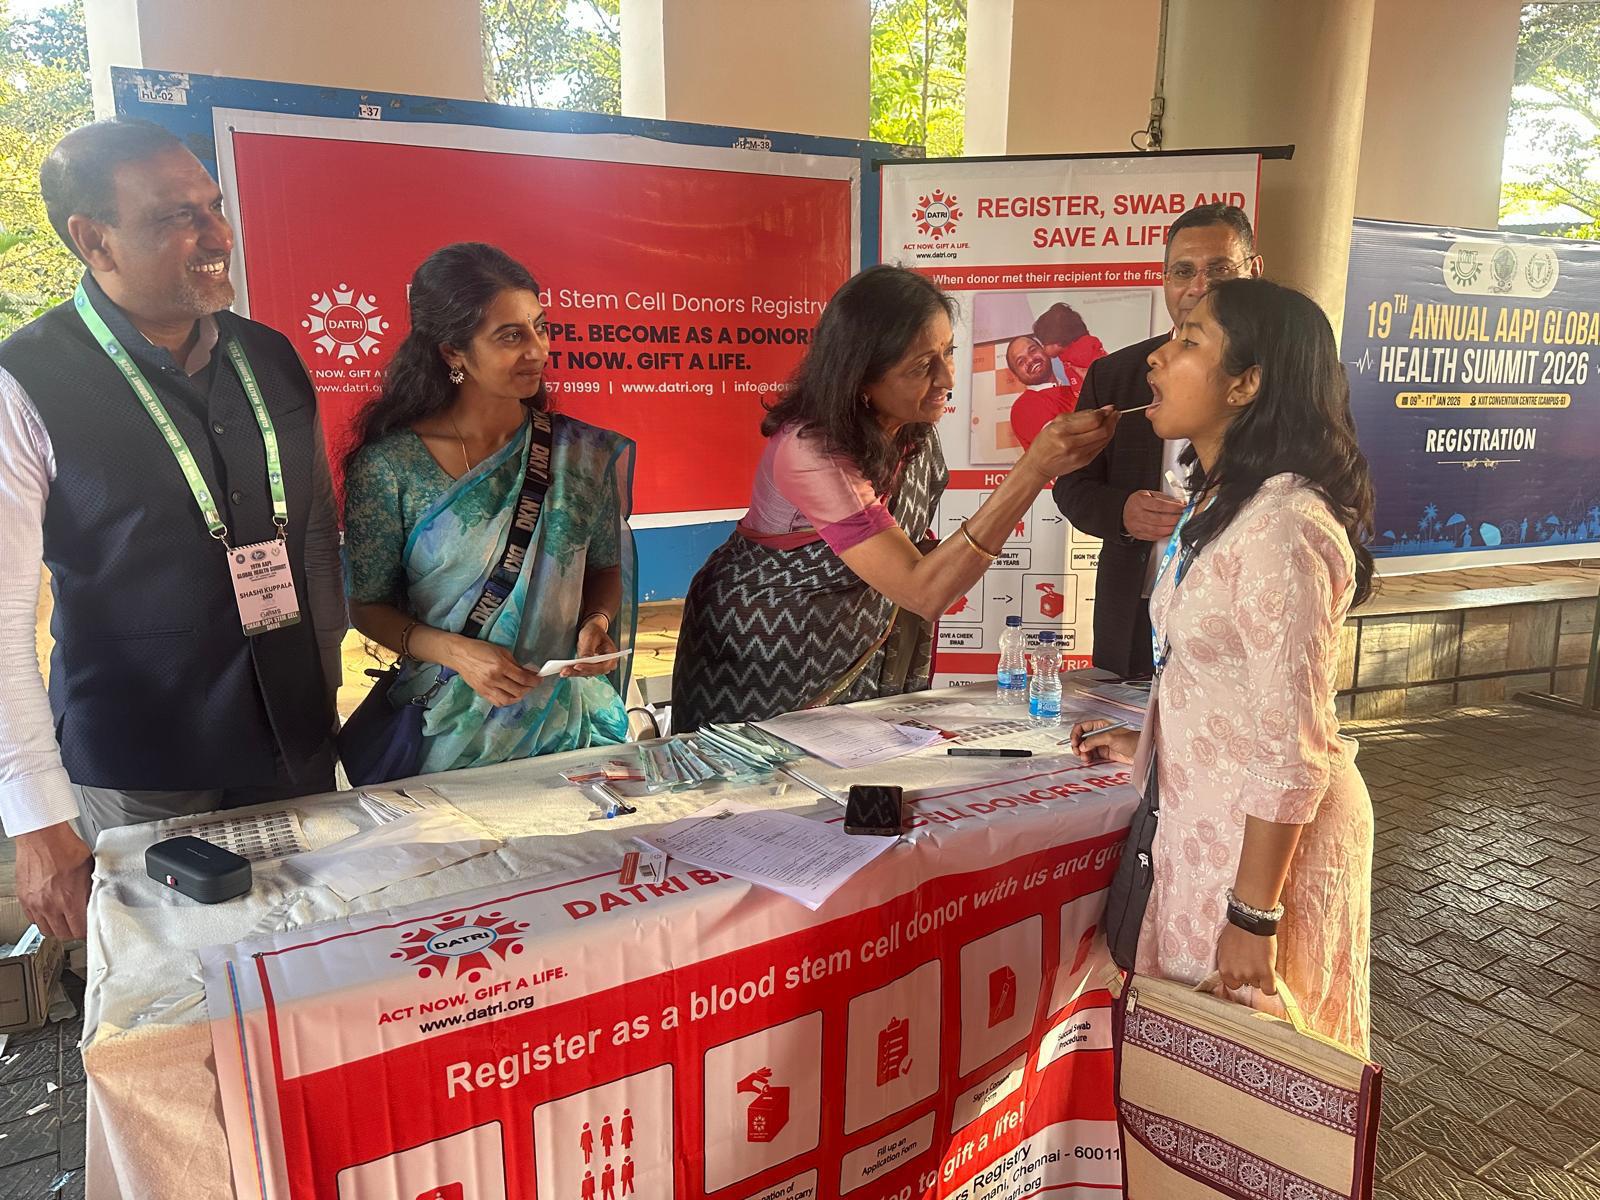 Dr. Hetal Gor, Chair of AAPI BOT, emphasized the need for commitment. She said, “You could be someone’s only match—their only hope. Registering is a serious promise, but the donation process is safe and complication-free.”
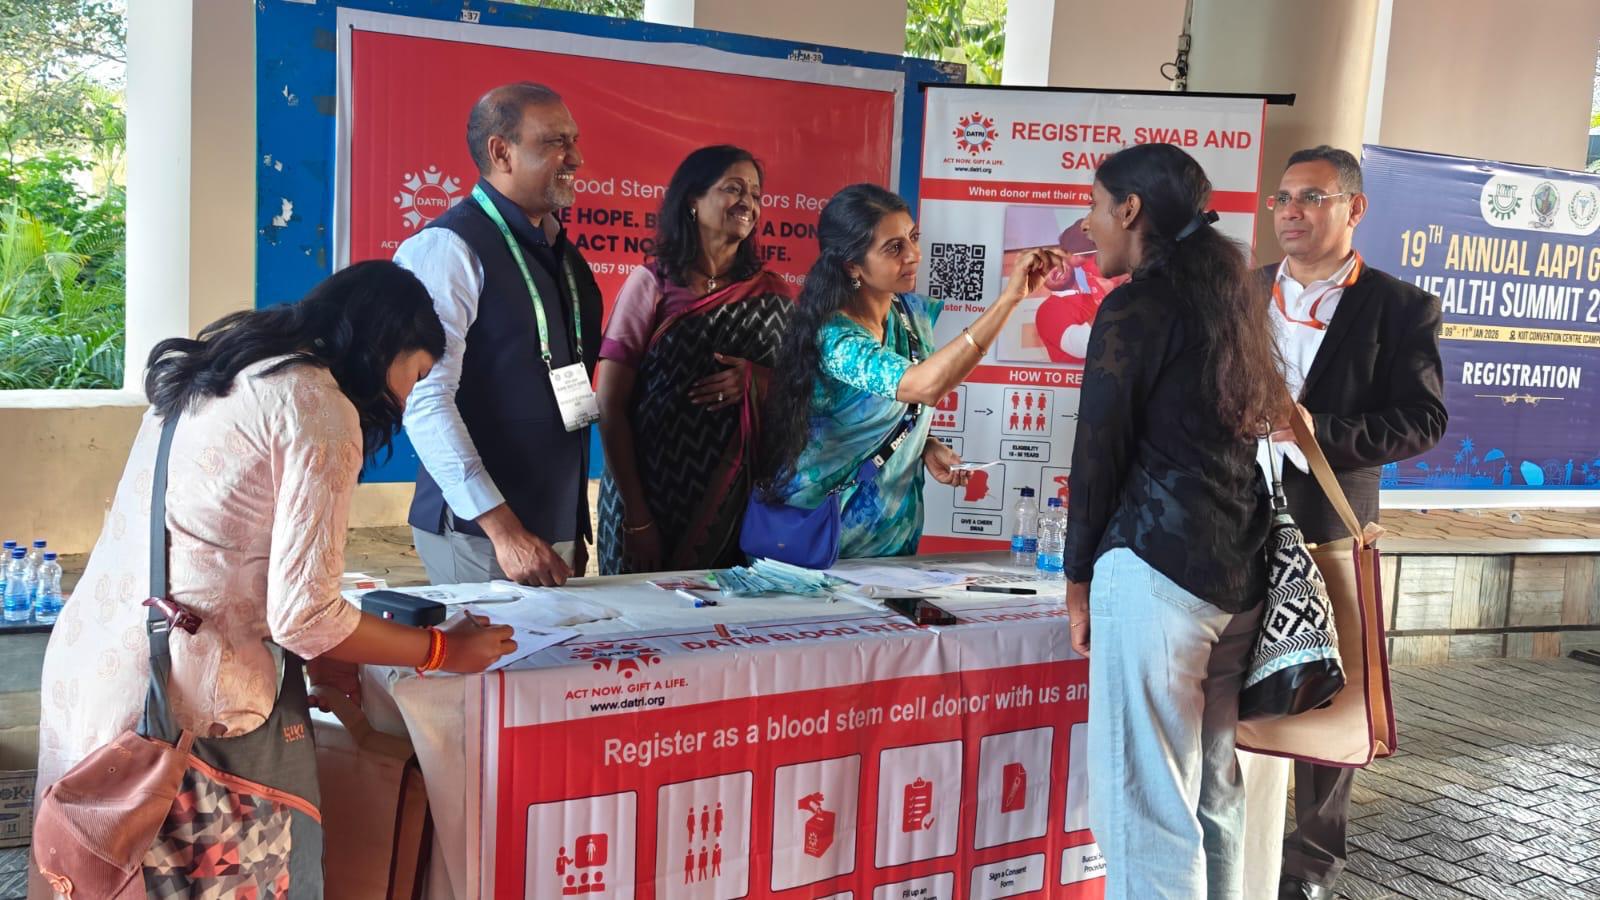 Dr. Krishan Kumar, Vice President-Elect, while highlighting the disparity, said, “70% of patients lack a family match. For Indians, the odds are even lower due to the limited donor pool.”
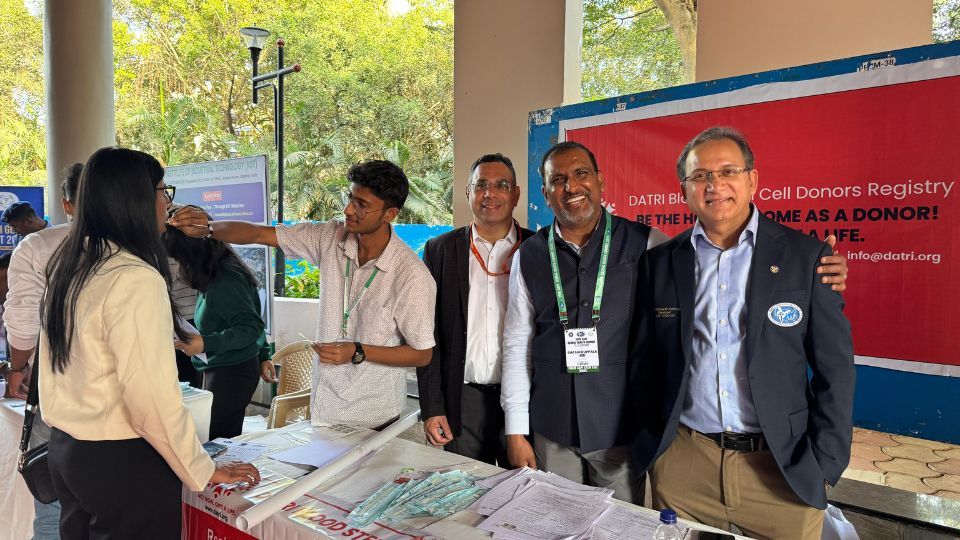 Dr. Sashi Kuppala, while explaining the science, said, Matching donors is based on HLA typing, which is inherited and ethnicity-specific. Thousands of patients rely on transplants to survive.” Dr. Kuppala pointed to the “tremendous response to this initiative from the AAPI members and the wider Indian community.”